Breaking News
 Is Big Pharma Selling Postpartum Depression to New Moms?
 Make Men Men Again: Low T Is Now a National Defense Problem
 Druski: They're Lying To You About Overnight Success!
 $6.27 Diesel Just Hit Harvest. The Grocery Aisle Hasn't Felt It Yet.
Top Tech News
 Tesla Model 3 killer charges from 10 to 97% in just 9 minutes
 World-first unpowered DNA computer sets speed record
 I Power 5 Buildings Off-Grid. Here's How
 The US government is pushing hard to get a working nuclear fission reactor into space by late 2028
 SpaceX Starmind AI in Space Radiator
 China Will Dominate Global Nuclear Energy Through 2035, Analyst Says
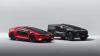 These Absolutely Wild-Looking EVs Are Saudi Arabia's First Homegrown Cars
 BEYOND THE MOON: NASA plans a nuclear-powered fleet to push DEEPER into space
 Big Oil Backs Mazama's $135 Million Bet On Superhot Geothermal
 Quantum compass takes flight on Northrop's Lumberjack drone
Adylkuzz cyberattack dwarfs WannaCry

The new attack targets the same vulnerabilities the WannaCry ransomware worm exploited but, rather than freeze files, uses the hundreds of thousands of computers believed to have been infected to mine virtual currency.
Following the detection of the WannaCry attack on Friday, "researchers at Proofpoint discovered a new attack linked to WannaCry called Adylkuzz," said Nicolas Godier, a researcher at the computer security firm.
This other very large-scale attack uses both EternalBlue and DoublePulsar to install the cryptocurrency miner Adylkuzz. Initial statistics suggest that this attack may be larger in scale than WannaCry, affecting hundreds of thousands of PCs and servers worldwide: because this attack shuts down SMB networking to prevent further infections with other malware (including the WannaCry worm) via that same vulnerability, it may have in fact limited the spread of last week's WannaCry infection.